How to Install Squid (Caching / Proxy) on CentOS 7
Squid is a caching and forwarding web proxy. It is most often used in conjunction with a traditional LAMP stack (Linux, Apache, MySQL, PHP), and can be used to filter traffic on HTTP, FTP, and HTTPS, and increase the speed (thus lower the response time) for a web server via caching.
Pre-Flight Check
These instructions are intended specifically for installing Squid on a single CentOS 7 node.
I’ll be working from a Liquid Web Core Managed CentOS 7 server, and I’ll be logged in as root.
Step #1 Install Squid
First, clean-up yum:
yum clean all
As a matter of best practice we’ll update our packages:
yum -y update
Installing Squid and related packages is now as simple as running just one command:
yum -y install squid
Configure Squid to Start on Boot
And then start Squid:
systemctl start squid
Be sure that Squid starts at boot:
systemctl enable squid
To check the status of Squid:
systemctl status squid
To stop Squid:
systemctl stop squid
To access squid settings access : /etc/squid/squid.com
My basic config:
http_access allow localhost manager
http_access deny manager

# We strongly recommend the following be uncommented to protect innocent
# web applications running on the proxy server who think the only
# one who can access services on "localhost" is a local user
#http_access deny to_localhost

#
# INSERT YOUR OWN RULE(S) HERE TO ALLOW ACCESS FROM YOUR CLIENTS
#

# Example rule allowing access from your local networks.
# Adapt localnet in the ACL section to list your (internal) IP networks
# from where browsing should be allowed
http_access allow localnet
http_access allow localhost

# And finally deny all other access to this proxy
http_access deny all

# Squid normally listens to port 3128
http_port 3128

# Uncomment and adjust the following to add a disk cache directory.
#cache_dir ufs /var/spool/squid 10000 16 256
cache_replacement_policy heap LFUDA
cache_swap_low 90
cache_swap_high 95
maximum_object_size_in_memory 100 MB
cache_dir aufs /var/spool/squid 40000 16 256
cache_mem 40000 MB

# Leave coredumps in the first cache dir
coredump_dir /var/spool/squid

#
# Add any of your own refresh_pattern entries above these.
#
That is all!
Easy Samba installation on RHEL/CentOS 7
Samba is a client/server system that implements network resource sharing for Linux and other UNIX computers. With Samba, UNIX files and printers can be shared with Windows clients and vice versa. Samba supports the Session Message Block (SMB) protocol. Nearly all Windows computers include SMB support with their internal network subsystems (NetBIOS in particular).
With an appropriately-configured Samba server on Linux, Windows clients can map drives to the Linux filesystems. Likewise, theSamba client on UNIX can connect to Windows shares by their UNC name. Although differences among various operating systems (such as filesystem naming conventions, end-of-line conventions, and authentication) can limit interoperability, Samba offers a generally serviceable mechanism for resource sharing on a heterogenous network.
In this tutorial we will show you how to install and configure Samba server on RHEL and CentOS 7 linux.
Install and configure Samba on Rhel/CentOS 7
To install samba packages enter following command:
#yum install samba samba-client samba-common -y
Now configure samba edit the file /etc/samba/smb.conf
#mv /etc/samba/smb.conf /etc/samba/smb.conf.bkp
#vi /etc/samba/smb.conf
and paste following line:
[global]
workgroup = WORKGROUP
server string = Samba Server %v
netbios name = centos
security = user
map to guest = bad user
dns proxy = no
#============================ Share Definitions ==============================
[Anonymous]
path = /samba/anonymous
browsable =yes
writable = yes
guest ok = yes
read only = no
Save the smb.conf file and restart the service:
#mkdir -p /samba/anonymous
#systemctl enable smb.service
#systemctl enable nmb.service
#systemctl restart smb.service
#systemctl restart nmb.service
Add these Iptables rules, so that samba will work perfectly:
#firewall-cmd --permanent --zone=public --add-service=samba
#firewall-cmd --reload
Change permission for samba share:
#chmod -R 0755 anonymous/
#chown -R nobody:nobody anonymous/
Further we need to allow the selinux for the samba configuration as follows:
#chcon -t samba_share_t anonymous/
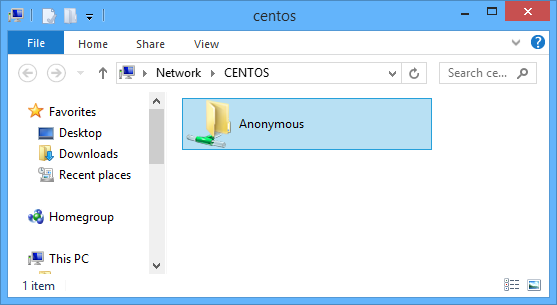
Now you can access the Centos 7.0 sharing in windows as follows, go to the Run prompt and type \centos :

Acesse \\centos
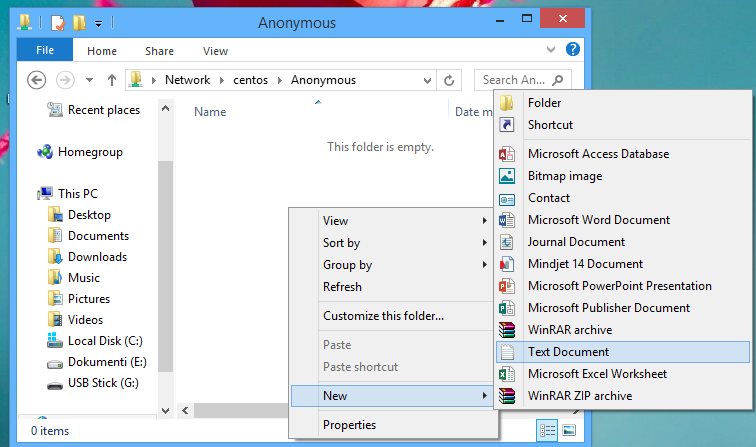
Now anonymous user can browse & create new text documents:
Secured samba server
For this I will create a group smbgrp & user rasho to access the samba server with proper authentication
#useradd rasho
#groupadd smbgrp
#usermod -a -G smbgrp rasho
#smbpasswd -a rasho
[root@localhost]# smbpasswd -a rasho
New SMB password: YOUR SAMBA PASS
Retype new SMB password: REPEAT YOUR SAMBA PASS
Added user rasho.
Create a new share, set the permission on the share:
#mkdir /home/secure
#chown -R rasho:smbgrp /home/secure/
#chmod -R 0770 /home/secure/
#chcon -t samba_share_t /home/secure/
Again edit the configuration file as :
#vi /etc/samba/smb.conf
Add the newly created samba share in smb.conf file:
[Secure]
path = /home/secure
valid users = @smbgrp
guest ok = no
writable = yes
browsable = yes

Restart the samba service:
#systemctl restart smb.service
#systemctl restart nmb.service
Now at windows machine check the folder now with the proper credentials
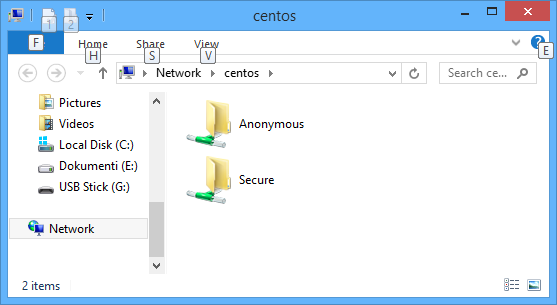
Open samba sharing

Create new text documents:
That is all!
How to configure Btrfs on Centos 7
Check unit to add
#fdisk -l
Return:
Exemplo:
Selecione o disco
Disk /dev/sdb: 17.2 GB, 17179869184 bytes, 33554432 sectors
Units = sectors of 1 * 512 = 512 bytes
Sector size (logical/physical): 512 bytes / 512 bytes
I/O size (minimum/optimal): 512 bytes / 512 bytes
Adding partition:
#fdisk /dev/sdb
# M – “Show all options available”
# P – “Type ” p” to display information on the disc as the current partitions”
# n – “Show all options available”
# p – “primary partition”
# 1 – “Partition number 1”
# enter – “default”
# enter – “default”
# w “List unit”
Check unit created
# fdisk -l
Check BTRFS Version and Installation
#yum search btrfs
#yum install btrfs-progs.x86_64
FSTAB access the file and add the mount point and compression
#vim /etc/fstab
Add the following line:
/dev/sdb1 /opt btrfs compress=zlib,compress-force=zlib 1 1
Assembling Compression :
#mkfs.btrfs /dev/sdb1 -f
Restart the machine and starting from this moment the unit / opt ‘ll be using btrfs to compress the files.
Install Cpanel/WHM on CentOS 7, RHEL 7
Here in this article we will discuss about latest cPanel & WHM Version 11.50 feature and prerequisites and installation on fresh CentOS 7 / RHEL 7 Version.
Latest Features of cPanel & WHM 11.50 :
CentOS , CloudLinux , and RHEL 7 support
Use the XFS or ext4 filesystems.
Less booting time
Greylisting feature : which protect server from unwanted emails and untrusted email servers .
Installation Recommended settings:
Disable OS Firewall before installation .
Recommended Hardware :
Minimum & Recommended Processor should be 226MHZ
Minimum RAM should be 1 GB.
Minimum Disk Space should be 20 GB .
Installation of cPanel in CentOS 7 / RHEL 7 / CloudLinux 7 :
Before doing cpanel & WHM installation first ensure your OS Version , RAM and diskspace.
Deactivate firewall on CentOS 7 , CloudLinux 7 and RHEL 7 :
# iptables-save > ~/iptables.rules
# systemctl stop firewalld.service
# systemctl disable firewalld.service
Disable Security Enhanced Features ( SELinux ) :
If your server running SELinux Features of security, then disable this features .
To disable , run the below command.
Edit the configuration file /etc/selinux/config and set the parameter SELINUX to disabled, below is my configuration file , after set the parameter you need to reboot the server.
# vim /etc/selinux/config

# This file controls the state of SELinux on the system.

# SELINUX= can take one of these three values:

#     enforcing - SELinux security policy is enforced.

#     permissive - SELinux prints warnings instead of enforcing.

#     disabled - No SELinux policy is loaded.

SELINUX=permissive

# SELINUXTYPE= can take one of these two values:

#     targeted - Targeted processes are protected,

#     minimum - Modification of targeted policy. Only selected processes are protected.

#     mls - Multi Level Security protection.

SELINUXTYPE=targeted
Installation set up steps :
cPanel installation need perl package , so we need to install perl before instaalation .
# yum install perl
After installation of perl, set the hostname of server , the hostname should be in FQDN i.e fully qualified domain name. Below is steps to set hostname in Centos / RHEL 7.
Below command to check hostname of server :
# hostnamectl
To set hostname :
#hostnamectl set-hostname cpanel.techtransit.org
Install cPanel/WHM
Now we will download cpanel script on home directory of server , which will install cpanel & WHM .Follow below steps for installation.
# cd /home
# curl -o latest -L https://securedownloads.cpanel.net/latest
# sh latest
Now script will run some hours and after installation you will get some output like , time taken in installation as well as server access url and access details, you will use in login root as a user and use password of root user.
You will get WHM access like below url.
ACCESS URL:
https://your –server-public-ip:2087/
OR
https://server-hostname:2087/
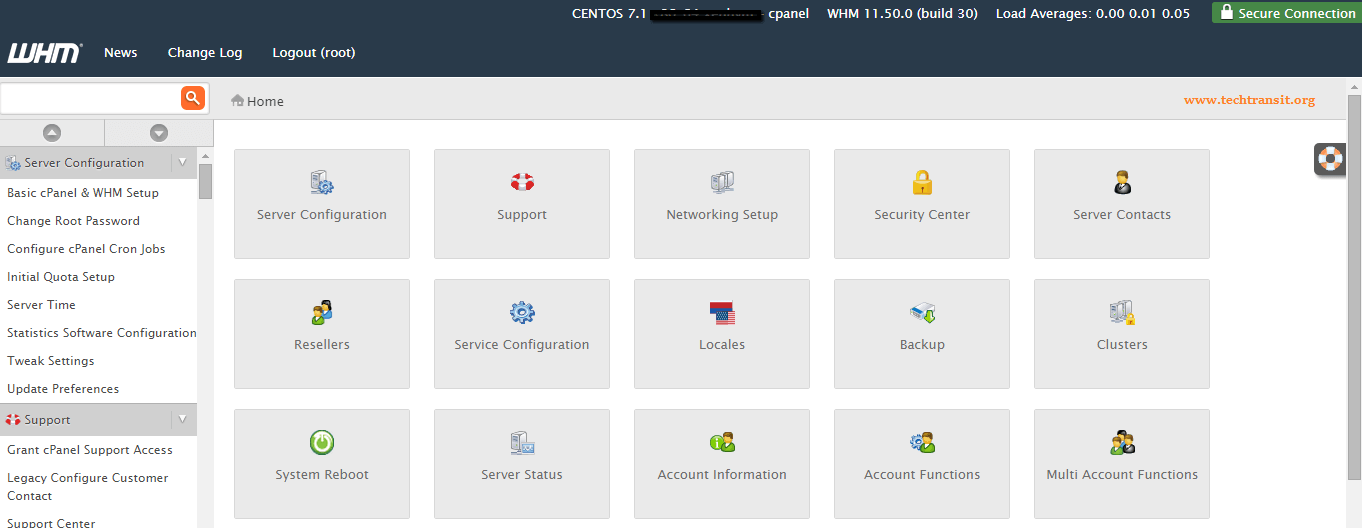
cpanel_11.50_centos7
After access of url in browser and put the username password details in access url and accept license agreement, you can configure server networking, ip address and nameserver as according to you , you should have good nice knowledge of System Admin part.
Hope you enjoy this post , for any concern please comment here and give us feedback. Thanks
Install Guacamole on CentOS 7
This post is for installing the latest version of Guacamole on CentOS 7, as there are several difference from the previous guide I did. If you want to read more about Guacamole, and how awesome it is, I recommend you take a glance at my previous post here.
**Note, I am installing the MySQL Authentication package which allows me to store connections and authentication information in a database, instead of a plain-text XML file.
Let’s Get Started!
1.) prerequisites:
yum -y install epel-release wget
wget -O /etc/yum.repos.d/home:felfert.repo http://download.opensuse.org/repositories/home:/felfert/Fedora_19/home:felfert.repo
yum -y install cairo-devel freerdp-devel gcc java-1.8.0-openjdk.x86_64 libguac libguac-client-rdp libguac-client-ssh libguac-client-vnc \
libjpeg-turbo-devel libpng-devel libssh2-devel libtelnet-devel libvncserver-devel libvorbis-devel libwebp-devel openssl-devel pango-devel \
pulseaudio-libs-devel terminus-fonts tomcat tomcat-admin-webapps tomcat-webapps uuid-devel
Above we are just installing adding the EPEL and Felfert repositories that contain the files we need, and installing all our prereqs. Easy.
2.) guacd install
mkdir ~/guacamole && cd ~/
wget http://sourceforge.net/projects/guacamole/files/current/source/guacamole-server-0.9.9.tar.gz
tar -xzf guacamole-server-0.9.9.tar.gz && cd guacamole-server-0.9.9
./configure --with-init-dir=/etc/init.d
make
make install
ldconfig
Guacamole is delivered in two different pieces. The back-end is what we just installed above, from source, called guacd (or guacamole daemon). The other piece is the guacamole client, or web frontend. This is delivered via Jetty, and installed next.
3.) guacamole client
mkdir -p /var/lib/guacamole && cd /var/lib/guacamole/
wget http://sourceforge.net/projects/guacamole/files/current/binary/guacamole-0.9.9.war -O guacamole.war
ln -s /var/lib/guacamole/guacamole.war /var/lib/tomcat/webapps/
rm -rf /usr/lib64/freerdp/guacdr.so
ln -s /usr/local/lib/freerdp/guacdr.so /usr/lib64/freerdp/
We now have the guacamole server daemon and the guacamole client installed. Next up is the MySQL Authentication piece, using MariaDB.
4.) mysql authentication
yum -y install mariadb mariadb-server
mkdir -p ~/guacamole/sqlauth && cd ~/guacamole/sqlauth
wget http://sourceforge.net/projects/guacamole/files/current/extensions/guacamole-auth-jdbc-0.9.9.tar.gz
tar -zxf guacamole-auth-jdbc-0.9.9.tar.gz
wget http://dev.mysql.com/get/Downloads/Connector/j/mysql-connector-java-5.1.38.tar.gz
tar -zxf mysql-connector-java-5.1.38.tar.gz
mkdir -p /usr/share/tomcat/.guacamole/{extensions,lib}
mv guacamole-auth-jdbc-0.9.9/mysql/guacamole-auth-jdbc-mysql-0.9.9.jar /usr/share/tomcat/.guacamole/extensions/
mv mysql-connector-java-5.1.38/mysql-connector-java-5.1.38-bin.jar /usr/share/tomcat/.guacamole/lib/
systemctl restart mariadb.service
The above is installing mariadb, downloading the needed .jar’s, and moving them to where they belong. All but one jar file is included in the Guacamole MySQL Auth download, which is the MySQL Java Connector.
5.) configure database
mysqladmin -u root password MySQLRootPass
mysql -u root -p   # Enter above password
create database guacdb;
create user 'guacuser'@'localhost' identified by 'guacDBpass';
grant select,insert,update,delete on guacdb.* to 'guacuser'@'localhost';
flush privileges;
quit
Here we created the database and user for guacd to use.
6.) extend database schema
cd ~/guacamole/sqlauth/guacamole-auth-jdbc-0.9.9/mysql/schema/
cat ./*.sql | mysql -u root -p guacdb   # Enter SQL root password set above
And here we extend the schema of the database we created.
7.) configure guacamole
mkdir -p /etc/guacamole/ && vi /etc/guacamole/guacamole.properties
The above is creating our needed directories, and then creating the guacamole.properties file. This file is what tomcat uses to know what port to talk to guacd on as well as how to access the database. Here is a basic guacamole.properties file that will do what you need.
# MySQL properties
mysql-hostname: localhost
mysql-port: 3306
mysql-database: guacdb
mysql-username: guacuser
mysql-password: guacDBpass

# Additional settings
mysql-default-max-connections-per-user: 0
mysql-default-max-group-connections-per-user: 0
This will configure guacamole to use the database and user that we created on the default port of 4822. Note, this is for internal communication only and is not the port that you will be accessing the web interface on.
And we have to create a symlink so Guacamole can find the config file:
ln -s /etc/guacamole/guacamole.properties /usr/share/tomcat/.guacamole/
8.) Cleanup
All that’s left is a little housecleaning!
cd ~ && rm -rf guacamole*
systemctl enable tomcat.service && systemctl enable mariadb.service && chkconfig guacd on
systemctl reboot
Once your server boots, you’ll have Guacamole running and ready to be used! Head on over to http://guac_server_ip:8080/guacamole to start using your new Guacamole server! default username and password are both ‘guacadmin’.
If you’re having trouble accessing the webpage for Guacamole, make sure you have configured firewalld (or disabled it) to allow access to port 8080.
Leave me some feedback!