Instalando Zabbix Agent no CentOS/RHEL 6 e 7

Olá amigos.
O agente Zabbix concentra as informações locais sobre o dispositivo monitorado para posterior envio ao servidor ou proxy Zabbix (dependendo da configuração). Em caso de falhas (como um disco cheio ou a interrupção de um processo) o servidor Zabbix pode alertar .
Existe inúmeros agentes como (FreeBSD, OpenBSD, Windows, Centos, Debian, openSUSE, Ubuntu, Ipmi, Jmx e SNMP).
Abaixo vamos realizar a simples instalação do Zabbix Agente .
Adicionar repositórios
Vamos executar os comandos abaixo conforme o seu SO para adicionar o Zabbix agente ao repositório
CentOS 6 execute o comando abaixo:
rpm -Uvh http://repo.zabbix.com/zabbix/4.0/rhel/6/x86_64/zabbix-release-4.0-1.el6.noarch.rpmCentOS 7 execute o comando abaixo:
rpm -Uvh http://repo.zabbix.com/zabbix/4.0/rhel/7/x86_64/zabbix-release-4.0-1.el7.noarch.rpmInstalando o Zabbix Agente
yum install zabbix-agentDefinindo o arquivo de configuração
Minha sugestão é deletar o arquivo original de configuração e criar um arquivo novo somente com as informações necessárias :
rm /etc/zabbix/zabbix_agentd.confAgora vamos criar o novo arquivo e informar as configurações necessarias:
vim /etc/zabbix/zabbix_agentd.confAdicione as linhas abaixo, lembrando de substituir o endereço do servidor zabbix e o nome do servidor monitorado:
PidFile=/var/run/zabbix/zabbix_agentd.pid
LogFile=/var/log/zabbix/zabbix_agentd.log
LogFileSize=0
DebugLevel=3
Server=IP DO SERVIDOR ZABBIX
StartAgents=5
ServerActive=IP DO SERVIDOR ZABBIX
Hostname=HOSTNAME DA MAQUINA MONITORADA
Timeout=3
Include=/etc/zabbix/zabbix_agentd.d/*.conf
Iniciando o serviço do Zabbix Agent
CentOS 6 execute o comando abaixo para habilitar a inicialização e subir o serviço:
# service zabbix-agent start
# chkconfig zabbix-agent on
CentOS 7 execute o comando abaixo para habilitar a inicialização e subir o serviço:
# systemctl start zabbix-agent
# systemctl enable zabbix-agent
Liberando as portas no iptables
Caso o firewall do servidor esteja habilitado é necessário executar o comando abaixo para liberação da porta de comunicação:
iptables -A INPUT -p tcp -s 192.168.1.100 --dport 10050 -m state --state NEW,ESTABLISHED -j ACCEPTLembrando que é necessario subistituir o ip do comando pelo o ip do seu server Zabbix.
Validando a Execução do Agente
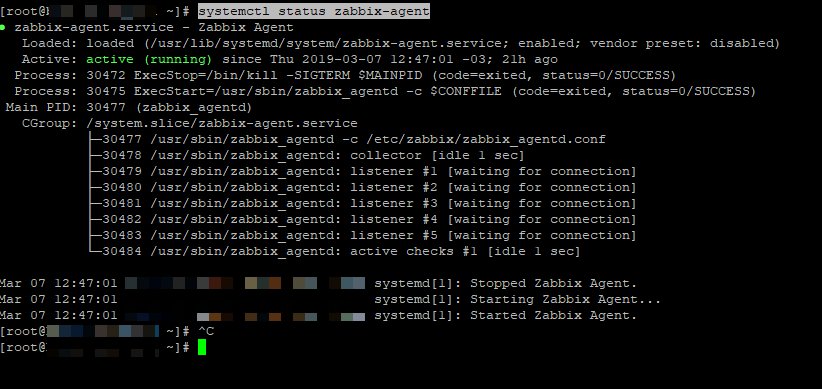
Execute o comando abaixo para validar a execução do Zabbix Agent :
systemctl status zabbix-agentConforme a imagem abaixo você pode ver que o serviço do Zabbix está rodando.
Bom pessoal o procedimento é simples e qualquer duvida estou a disposição.
Abraços
Como monitorar MYSQL/MariaDB com Zabbix
Olá amigos.
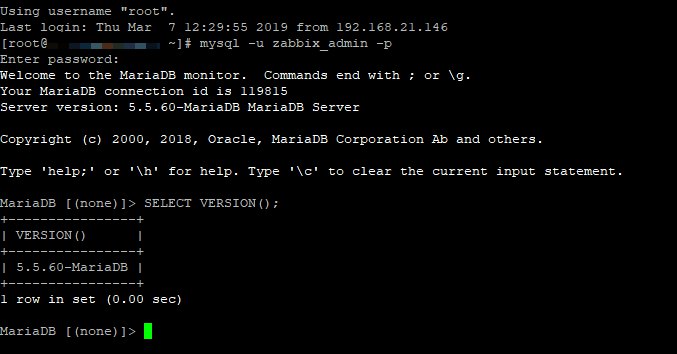
Estaremos configurando o Zabbix server para realizar o monitoramento de um servidor de aplicação Linux com o Centos 7 que atualmente está executando uma aplicação WEB no MariaDB.
Preparação do Banco de Dados
Primeiro teremos que executar as querys abaixo no banco para preparação do mesmo para monitoramento:
Conectar no banco de dados:
mysql -u root -pCriando usuário no banco para o Zabbix poder executar as querys de monitoramento:
create user 'zabbix_admin'@'localhost' IDENTIFIED BY 'Password';Rodando o comando para conceder os privilégios ao usuário:
GRANT USAGE ON *.* TO 'zabbix_admin'@'localhost' IDENTIFIED BY 'Password';Atualizando as liberações realizadas:
flush privileges;Após executado os comandos acima basta aplicar o comando abaixo para desconectar do banco e voltar ao SO. Lembrete, faça a definição da sua senha para o usuario zabbix_admin no campo ‘Password’ informado no Script.
exitConfigurando o Cliente
Lembrete, é necessário ter o Zabbix Agent instalado no servidor .
Para monitorar o MySql / MariaDB nós temos que criar um arquivo chamado userparameter_mysql.conf em /etc/zabbix/zabbix_agentd.conf.d/
O arquivo conterá as configurações para coletar os dados:
vim /etc/zabbix/zabbix_agentd.conf.d/userparameter_mysql.confAdicione as linhas abaixo dentro do arquivo criado:
# For all the following commands HOME should be set to the directory that has .my.cnf file with password information.
#
# Flexible parameter to grab global variables. On the frontend side, use keys like mysql.status[Com_insert].
# Key syntax is mysql.status[variable].
UserParameter=mysql.status[*],echo "show global status where Variable_name='$1';" | HOME=/etc/zabbix mysql -N | awk '{print $$2}' # My line
#
# Flexible parameter to determine database or table size. On the frontend side, use keys like mysql.size[zabbix,history,data].
# Key syntax is mysql.size[<database>,<table>,<type>].
# Database may be a database name or "all". Default is "all".
# Table may be a table name or "all". Default is "all".
# Type may be "data", "index", "free" or "both". Both is a sum of data and index. Default is "both".
# Database is mandatory if a table is specified. Type may be specified always.
# Returns value in bytes.
# 'sum' on data_length or index_length alone needed when we are getting this information for whole database instead of a single table
UserParameter=mysql.size[*],echo "select sum($(case "$3" in both|"") echo "data_length+index_length";; data|index) echo "$3_length";; free) echo "data_free";; esac)) from information_schema.tables$([[$
#
#Default below
UserParameter=mysql.ping,HOME=/etc/zabbix mysqladmin ping | grep -c alive
#
#My line
UserParameter=mysql.uptime,HOME=/etc/zabbix mysqladmin status | cut -f2 -d ":" | cut -f1 -d "T" | tr -d " "
UserParameter=mysql.threads,HOME=/etc/zabbix mysqladmin status | cut -f3 -d ":" | cut -f1 -d "Q" | tr -d " "
UserParameter=mysql.questions,HOME=/etc/zabbix mysqladmin status | cut -f4 -d ":"|cut -f1 -d "S" | tr -d " "
UserParameter=mysql.slowqueries,HOME=/etc/zabbix mysqladmin status | cut -f5 -d ":" | cut -f1 -d "O" | tr -d " "
UserParameter=mysql.qps,HOME=/etc/zabbix mysqladmin status | cut -f9 -d ":" | tr -d " "
UserParameter=mysql.version,mysql -V
Em seguida, precisamos fornecer ao Zabbix as informações de login para nosso novo usuário. Crie um arquivo chamado .my.cnf em /etc/ zabbix/
vim /etc/zabbix/.my.cnfAdicione as linhas abaixo, lembrando de substituir o password pela senha definida.
#
[mysql]
user=zabbix_admin
password=Password
[mysqladmin]
user=zabbix_admin
password=Password
Reinicie o serviço do agente zabbix usando o seguinte comando:
systemctl restart zabbix-agentPronto, até este momento a parte do cliente e agente estão prontas. Agora precisamos preparar o Zabbix Server para monitorar este host.
Configurando o Zabbix Server
É necessário que seja selecionado o template do MYSQL no host monitorado conforme imagem abaixo:

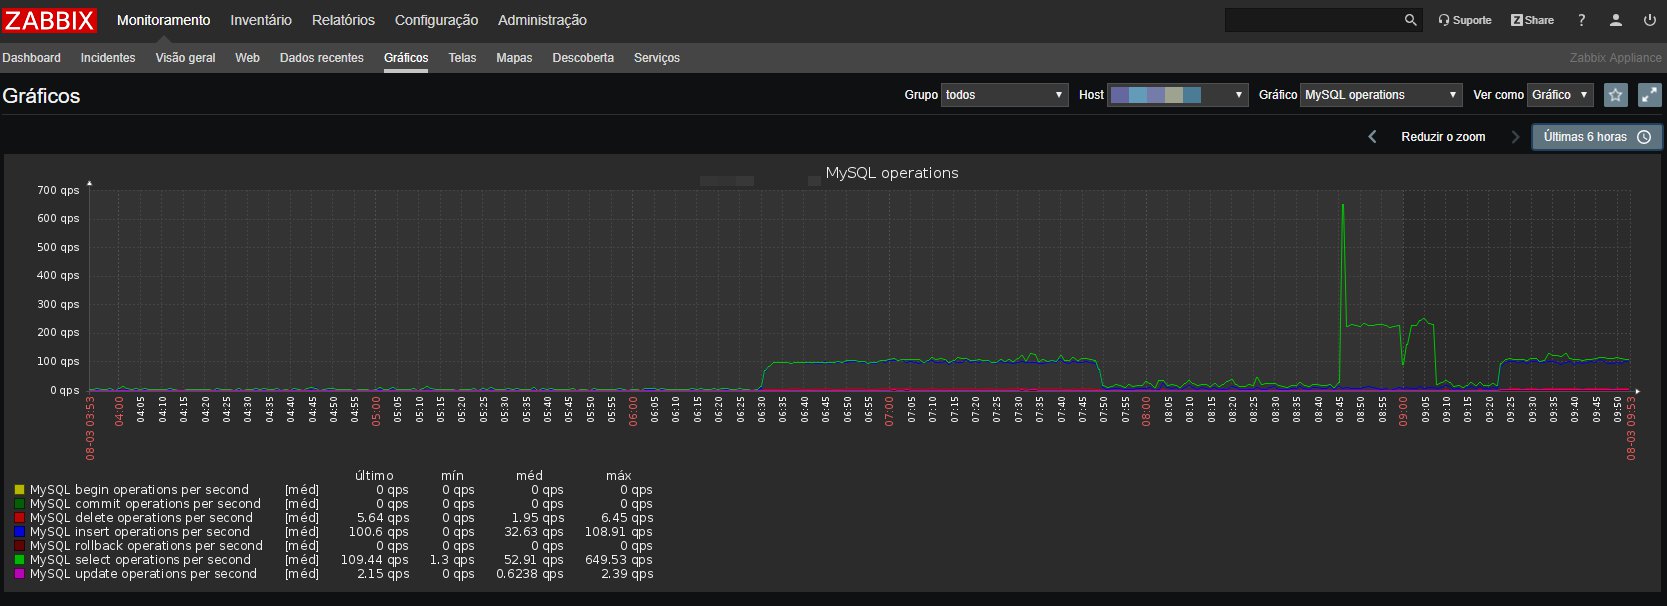
Após a inclusão do template é importante lembrar que a primeira coleta e visão dos dados pode demorar até uma hora dependendo das configurações do ambiente. Abaixo um exemplo da visão do servidor monitorado com a configuração que realizamos
O setup foi simples e creio que seja interessante utilizar nos servidores que possuem banco de dados local .
Qualquer duvida estou a disposição. Abraços
Script para automatizar a instalação do Zabbix Agente

Olá Amigos.
Recentemente venho trabalhando bastante com o Zabbix que me surpreendeu pela eficiência e facilidade que a ferramenta tem de se moldar ao seu ambiente.
O agente Zabbix é instalado no dispositivo a ser monitorado, também monitora ativamente os recursos e aplicações locais (discos e partições, memória, estatísticas do processador, etc).
O que mais me chama atenção é que o agente Zabbix são muito eficientes pois utilizam chamadas nativas do sistema operacional para obter as informações estatísticas.
O agente Zabbix é suportado por:
• Linux
• IBM AIX
• FreeBSD
• NetBSD
• OpenBSD
• HP-UX
• Mac OS X
• Solaris: 9, 10, 11
• Windows: 2000, Server 2003, XP, Vista, Server 2008, 2012, 2016 , 7 , 8 10
O problema:
Há alguns dias tive o problema de ter que publicar para todos os servidores da empresa o Zabbix, e a ideia que tive foi fazer um script para copiar os executáveis do monitoramento e criar o arquivo de configuração pegando o nome do servidor e passando para o arquivo de configuração.
Depois do script criado a minha ideia foi utilizar um GPO para aplicar esse script para OU que contem os servidores. Basicamente uma solução rápida.
Segue abaixo o script:
@echo off
REM #
REM #versao mark-v0.2#
REM #
REM #NOME#
REM #instala_zabbix.exe#
REM #
REM #DESCRICAO#
REM #Instalao Zabbix via rede nos servidores Windows#
REM #
REM #
REM #GERALDO LUCAS POLI (27/07/2018)#
REM # Verifica existencia diretório Zabbix #

REM #MODULO 1#
IF EXIST "c:\Zabbix\zabbix_agentd.exe" (exit) ELSE (echo "Iniciando a instalacao do Zabbix Agent")
REM #
REM # Exibe mensagem na tela#
echo Copiando Arquivos

REM #MODULO 2 - Criar o diretório na máquina#
mkdir c:\zabbix
echo Pasta zabbix criada no C:

REM #MODULO 3 - Realiza a cópia dos binários para o sistema#
xcopy \\192.168.2.12\zabbix\zabbix_agents_3.4.6.win\bin\win64\zabbix_agentd.exe c:\zabbix\
xcopy \\192.168.2.12\zabbix\zabbix_agents_3.4.6.win\bin\win64\zabbix_get.exe c:\zabbix\
xcopy \\192.168.2.12\zabbix\zabbix_agents_3.4.6.win\bin\win64\zabbix_sender.exe c:\zabbix\

REM #MODULO 4 *PUNK* - Cria arquivo de configuração e define nome do servidor #
echo Criando Arquivos de configuracao
echo Server=192.168.1.26 > c:\zabbix\zabbix_agentd.conf
echo Hostname=%COMPUTERNAME% >> c:\zabbix\zabbix_agentd.conf
echo StartAgents=5 >> c:\zabbix\zabbix_agentd.conf
echo DebugLevel=3 >> c:\zabbix\zabbix_agentd.conf
echo LogFile=c:\zabbix\zabbix_agentd.log >> c:\zabbix\zabbix_agentd.conf
echo Timeout=5 >> c:\zabbix\zabbix_agentd.conf
echo EnableRemoteCommands=1 >> C:\zabbix\zabbix_agentd.conf

REM #MODULO 4 - Ajustes Finais #
echo Instalando o Serviço
C:\zabbix\zabbix_agentd.exe -i -c C:\zabbix\zabbix_agentd.conf
C:\zabbix\zabbix_agentd.exe -s -c C:\zabbix\zabbix_agentd.conf
echo As configuracoes para o servidor %COMPUTERNAME% foram criadas em %date% as %time%
echo As configuracoes para o servidor %COMPUTERNAME% foram criadas em %date% as %time% > c:\Zabbix\inst_agent.log
pause
Link do código sempre atualizado no GIT:
Considerações:
Podemos ver que o script é bem simples.
Dividi ele em 4 módulos para ficar mais fácil o entendimento, qualquer duvida estou a disposição.
Até a próxima.
Como instalar o Cacti no Centos7/RedHat7

Olá amigos, satisfação em escrever novamente para vocês.
Hoje veremos sobre o Cacti que é uma ferramenta software livre administrativa de rede, que recolhe e exibe informações sobre o estado de uma rede de computadores através de gráficos, permitindo o monitoramento e gerenciamento de redes simples até redes complexas, com centenas de dispositivos. Foi desenvolvido para ser flexível de modo a se adaptar facilmente a diversas necessidades, bem como ser robusto e adicionando a isto uma interface Web intuitiva e fácil de usar. Monitora o estado de elementos de rede e programas bem como largura de banda utilizada e uso de CPU.
Instalando Apache
yum install httpd httpd-devel
Instalando MariaDB
yum install mariadb-server -y
Instalando PHP
yum install php-mysql php-pear php-common php-gd php-devel php php-mbstring php-cli
Instalando PHP-SNMP
yum install php-snmp
Instalando NET-SNMP
yum install net-snmp-utils net-snmp-libs
Instalando RRDTool
yum install rrdtool
Iniciando Apache, MySQL e SNMP Services
systemctl start httpd.service
systemctl start mariadb.service
systemctl start snmpd.service
Configurando a inicialização com Sistema
systemctl enable httpd.service
systemctl enable mariadb.service
systemctl enable snmpd.service
Repositório + Nginx
yum install epel-release
yum install nginx
Instalando Cacti
yum install cacti
Definindo senha MYSQL
mysqladmin -u root password flisol2018
Acessar MYSQL:
mysql -u root -p
Rodar a Query
create database cacti;
GRANT ALL ON cacti.* TO cacti@localhost IDENTIFIED BY 'flisol';
GRANT ALL PRIVILEGES ON * . * TO 'cacti'@'localhost';
FLUSH privileges;
quit;
Criando tabelas
rpm -ql cacti | grep cacti.sql
mysql -u cacti -p cacti < /usr/share/doc/cacti-1.1.36/cacti.sql
Configurar conexão banco:
vim /etc/cacti/db.php
$database_type = "mysql";
$database_default = "cacti";
$database_hostname = "localhost";
$database_username = "cacti";
$database_password = "your-password-here";
$database_port = "3306";
$database_ssl = false;
Liberações Firewall
firewall-cmd --permanent --zone=public --add-service=http
firewall-cmd --reload
Configurando o Apache para aceitar as conexões
vim /etc/httpd/conf.d/cacti.conf
# httpd 2.4
Require all granted
# httpd 2.2
Order deny,allow
Deny from all
Allow from all
Reiniciar Apache
systemctl restart httpd.service
mysql_tzinfo_to_sql /usr/share/zoneinfo | mysql -u root -p mysql
Configurar Timezone no PHP
vim /ete/php.ini
date.timezone = "America/Sao_Paulo"
Habilitar a coleta dos graficos
sudo -u cacti /usr/bin/php /usr/share/cacti/poller.php
Acessando Aplicação:
Você deve abrir no navegador o endereço de ip apontando para o cacti, exemplo:
http://IP/cacti/
Algumas confirmações serão necessárias na interface web para concluir a instalação, após concluir a configuração da instalação a interface web será aberta:

Pronto, sua instalação está realizada.
Estaremos criando um próximo artigo aonde mostra a configuração dos relatórios e equipamento para iniciar a analise com o Cacti.
Qualquer duvida estou a disposição.
Abraços
Instalando Open-AudIT no Centos7/RedHat 7

Olá amigos, satisfação em escrever novamente para vocês.
Hoje veremos de maneira simples a instalação da ferramenta Open-AudIT no Linux.
O Open-AudIT também é suportado no Windows, porem não chegaremos a entrar neste método de instalação devido a performance da aplicação que ao ser executada no linux é superior ao Windows nesta situação.
Sistemas linux suportados: RedHat,Centos,Debian e Ubuntu.
Funcionalidades da Ferramenta
Open-AudIT é uma ferramenta de código livre que permite os administradores realizarem inventários de sua infraestrutura.
A propagação do agente pode ser realizado através de GPO para todos os computadores e servidor do domínio, assim a gestão de todos os ativos da sua rede podem ser controladas pela ferramenta.
Iniciando a instalação
Primeiramente se você tiver uma instalação mínima do Centos ou RedHat, provavelmente será necessário instalar o pacote perl-core para poder executar o instalador.
yum install perl-core
SELinux
Caso o SELinux estiver rodando e ativo é necessário desativá-lo.
Parando a execução
setenforce 0
Para que não seja iniciado após uma reinicialização, edite o arquivo /etc/sysconfig/config e altere a linha:
SELINUX=enforcing
alterar para:
SELINUX=permissive
Firewall
Para desativar firewall completamente, execute os seguintes comandos:
service firewalld stop
Evitar a inicialização com SO:
chkconfig firewalld off
Instalando o Apache
yum install httpd -y
Agora, inicie o serviço Apache e ativá-lo na inicialização:
systemctl start httpd.service
systemctl enable httpd.service
Instalando o MySQL (MariaDB)
yum install mariadb-server mariadb -y
Quando a instalação for concluída, inicie o MariaDB e ative-a no boot:
systemctl start mariadb
systemctl enable mariadb
Depois de iniciar o MariaDB, execute o script de segurança inicial para remover alguns padrões arriscados:
mysql_secure_installation
Instalando o PHP
yum install php php-mysql -y
Para que o Apache reconheça o mecanismo PHP, reinicie-o:
systemctl restart httpd.service
Instalando o OpeAudIT
Realizando o Download do instalador:
wget http://dl-openaudit.opmantek.com/OAE-Linux-x86_64-release_2.1.1.run
Tornando o arquivo executável.
chmod +x "nome do arquivo"
Iniciando a instalação:
./"nome do arquivo"
Resumo do log da instalação:
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Open-AudIT (1.4.0) Installation script
++++++++++++++++++++++++++++++++++++++++++++++++++++++
This installer will install Open-AudIT into /usr/local/omk.
To select a different installation location please rerun the installer with the -t option.
Ok to proceed with installation?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
++++++++++++++++++++++++++++++++++++++++++++++++++++++
performing pre-installation steps
++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Opmantek daemon init scripts detected
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Ok to shut down running Opmantek daemons for the duration of the installation?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Looking for old installations...
++++++++++++++++++++++++++++++++++++++++++++++++++++++
An old legacy installation was detected.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
The installer has found a pre-existing installation of one or more
Opmantek products in /usr/local/omk.
The installation can proceed but may cause disruptions to installed legacy products other than Open-AudIT.
If you agree to continue, the installer will take a backup snapshot of your complete previous installation and then prepare the installation environment for Open-AudIT.
Do you want to continue the installation?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Creating legacy snapshot, please wait...
Snapshot created, file name: /root/omk-legacy-2014-08-20.tgz
The installer has created a full snapshot of your previous installion in /root/omk-legacy-2014-08-20.tgz. The installation of Open-AudIT will now proceed.
Should you need to revert to your previous installation status, simply remove all contents of /usr/local/omk and unpack the snapshot:
rm -rf /usr/local/omk/* && tar -C / -xzvf /root/omk-legacy-2014-08-20.tgz
Hit <Enter> when ready to continue:
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Checking the Open-AudIT dependencies
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Required package mysql-server is installed.
Required package apache2 is installed.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Required packge apache2-utils is not installed.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Open-AudIT requires package apache2-utils to be installed and configured.
Do you want to install this package now?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Using apt-get to install apache2-utils
Required package libapache2-mod-proxy-html is installed.
Required package libapache2-mod-php5 is installed.
Required package openssh-client is installed.
Required package php5 is installed.
Required package php5-ldap is installed.
Required package php5-mcrypt is installed.
Required package php5-mysql is installed.
Required package php5-snmp is installed.
Required package nmap is installed.
Required package zip is installed.
Required package wget is installed.
Required package curl is installed.
Required package sshpass is installed.
Required package screen is installed.
Required package smbclient is installed.
Required package logrotate is installed.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Required packge libtime-parsedate-perl is not installed.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Open-AudIT requires package libtime-parsedate-perl to be installed and configured.
Do you want to install this package now?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Using apt-get to install libtime-parsedate-perl
-------COMMAND RETURNED EXIT CODE 100--------
apt-get -yq install libtime-parsedate-perl Reading package lists... Building dependency tree... Reading state information... E: Unable to locate package libtime-parsedate-perl
----------------------------------------
Looking for an existing Open-AudIT Community installation...
Do you want to perform a backup of your Open-AudIT installation?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Backing up database openaudit
Open-AudIT Backup created successfully, file name: /root/open-audit-backup-2014-08-20.tgz
++++++++++++++++++++++++++++++++++++++++++++++++++++++
copying files
++++++++++++++++++++++++++++++++++++++++++++++++++++++
........................................................................................................................................................................................................................................................................
++++++++++++++++++++++++++++++++++++++++++++++++++++++
done copying files
++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++
performing post-installation operations
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Open-AudIT needs the live configuration files in /usr/local/omk/conf/, and ships the defaults in /usr/local/omk/install/. If you agree, the installer will copy all missing files to the live configuration directory - it will not overwrite any files that are already present.
Ok to copy new or missing config files into the live configuration directory?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Init script for Opmantek daemon already present.
Installing conveniece symlinks
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Updated logrotation config file omk-rotate.conf available
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Ok to install the updated logrotation config file omk-rotate.conf?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Updated logrotation config file open-audit-rotate.conf available
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Ok to install the updated logrotation config file open-audit-rotate.conf?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Upgrading Opmantek Modules file
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Adjusting users, ownerships and permissions
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Priming remaining directories
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Configuration Updates
++++++++++++++++++++++++++++++++++++++++++++++++++++++
The new version of Open-AudIT may have introduced new configuration items, which can be added automatically (with their default settings).
Do you want to import any new configuration settings now?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Updating common config with new defaults.
Apache config directory unknown or non-existent, cannot install proxy config file!
Please note that the GUI for your Open-AudIT installation will only be available
at the URL http://localhost:8042/ until you configure Apache, and enable the Apache proxy with the config file ./install/04omk-proxy.conf or equivalent.
Hit <Enter> when ready to continue.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Installing Open-AudIT files
++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Copying Open-AudIT Web files
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Upgrade of existing Open-AudIT installation, no database initialisation required.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
performing final update operations
++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Adjusting Open-AudIT for standalone operation
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Adjusting Login Banner
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Detecting Configuration Changes
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Would you like to see an overview of all changed configuration items?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Performing config diff check, please wait...
Can't locate Time/ParseDate.pm in @INC (you may need to install the Time::ParseDate module) (@INC contains: /usr/local/omk/bin/../lib /etc/perl /usr/local/lib/perl/5.18.2 /usr/local/share/perl/5.18.2 /usr/lib/perl5 /usr/share/perl5 /usr/lib/perl/5.18 /usr/share/perl/5.18 /usr/local/lib/site_perl .) at /usr/local/omk/bin/../lib/OMK/Common.pm line 74.
BEGIN failed--compilation aborted at /usr/local/omk/bin/../lib/OMK/Common.pm line 74.
Compilation failed in require at /usr/local/omk/bin/opdiffconfigs.pl line 40.
BEGIN failed--compilation aborted at /usr/local/omk/bin/opdiffconfigs.pl line 40.
The configuration comparison tool has detected some differences between the shipped defaults (in /usr/local/omk/install) and the active settings (in /usr/local/omk/conf).
The affected files are:  opModules.nmis opCommon.nmis
A detailed listing of these differences has been saved in /tmp/Open-AudIT-config-diffs-2014-08-20.
You should review those differences (using less or an editor like nano, vi or emacs) and adjust your configuration settings accordingly.
Hit <Enter> when ready to continue:
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Opmantek Daemon Startup
++++++++++++++++++++++++++++++++++++++++++++++++++++++
The Opmantek daemon can now be started. It needs to be active to provide the Open-AudIT GUI, but you might want to delay that operation until you have adjusted the configuration files.
Do you want to start the Opmantek daemon now?
Type 'y' or hit <Enter> to accept, any other key for 'no': y
Starting OMKD
opEvents not installed or opEvents daemon init script not installed as /etc/init.d/opeventsd.
opConfig not installed or opConfig daemon init script not installed as /etc/init.d/opconfigd.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
Open-AudIT is Ready for Configuration
++++++++++++++++++++++++++++++++++++++++++++++++++++++
This initial installation of Open-AudIT is now complete.
However, to configure and fine-tune the application suitably for your environment you will need to make certain configuration adjustments.
We highly recommend that you visit the documentation site for Open-AudIT at https://community.opmantek.com/display/OA/Home which will help you to determine what configuration changes may be required for your environment.
If you have started the Opmantek daemon, then your new Open-AudIT dashboard should now be accessible at http://<HOSTNAME_OR_IP>/omk/oae/
If your browser is running on the same machine as Open-AudIT was installed onto, this would be http://localhost/omk/oae/
++++++++++++++++++++++++++++++++++++++++++++++++++++++
installation complete.
++++++++++++++++++++++++++++++++++++++++++++++++++++++
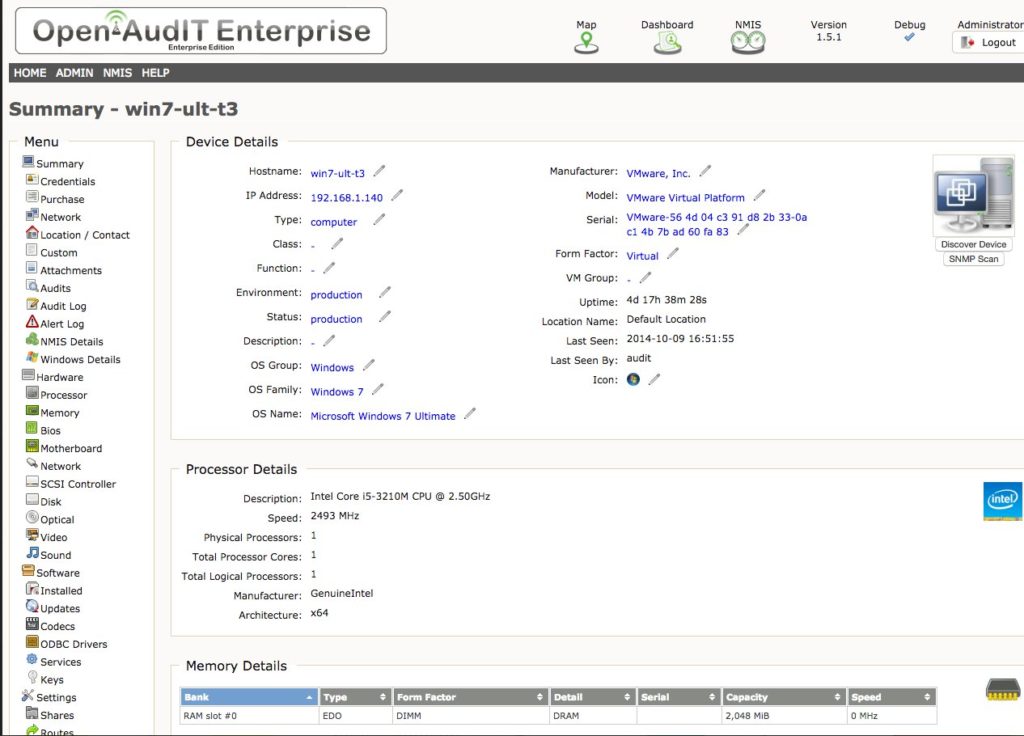
Acessando a interface WEB
http://IP>/omk/oae/
Conclusão
A interface WEB tem varias funcionalidades que é bacana ser estudadas.
Para gestão de grandes ambientes você pode realizar seperação por grupos e criar varias visões customizadas.
Espero que todos gostem e qualquer duvida estou a disposição. Abraços