Set Timezone in PHP
Some applications in PHP, can give a problem if you do not find the variable timezone set in php.ini, because they do not consult local timezone of the server.
To solve this, we set the timezone in PHP configuration file: php.ini.
Look for your php.ini file:
# Find / -name php.ini
Generally, it is located in /etc/php.ini.
Edit and change the timezone setting:
Find the date.timezone line and leave it below:
From:; date.timezone =
For:
date.timezone = America / Sao_Paulo
If your timezone is another, just change the America / Sao_Paulo parameter to your timezone.
The timezones list can be found here:
That’s All!.
How to Install Plugin Mirage in Cacti
Prerequisites:
Cacti version 0.8.8+ It may work on previous versions, but we haven’t tested against them.
PIA version 3.1
Download Mirage Plugin 1.2.0
Dowload Mega URL: https://mega.nz/#F!joBCSajS
Key: !5xOf-FjcDAkkS3K2TkAkTA
Installation:
Move the folder mirage to CACTI_HOME/plugins/
Ensure permission are correct (CACTI_HOME/plugins/mirage)
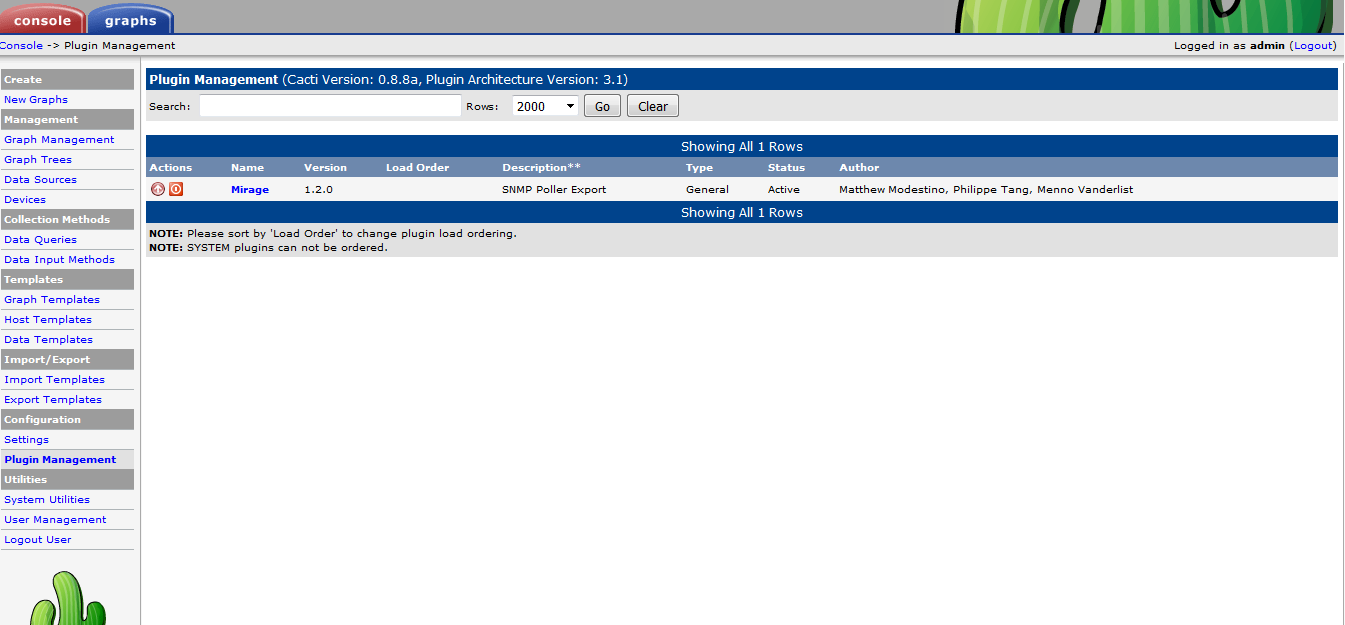
Install Mirage through Cacti Plugin Management /Enable Mirage pluging through Cacti Plugin Management
Review and save Mirage settings
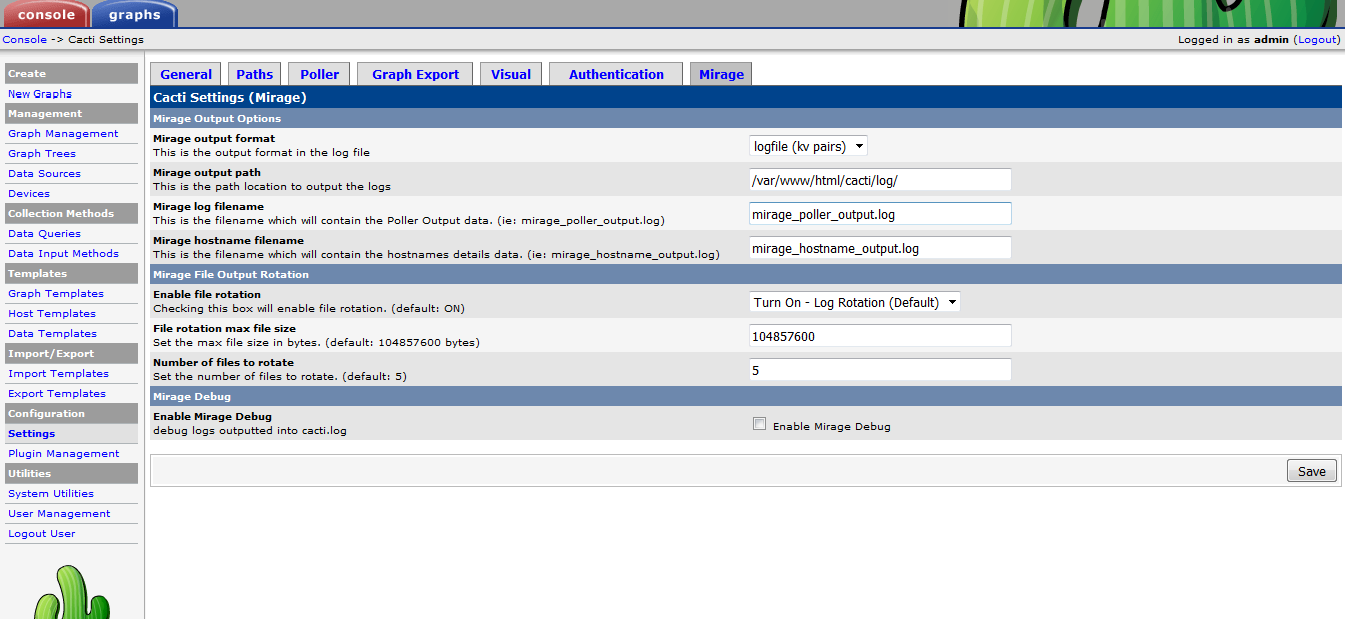
After installation it should generate a file called ” mirage_poller_output.log ” within the / var / www / html / cacti / log /
That is all!
Install Nagios 4.0.4 on Centos 7
For RHEL/CentOS users:
#yum install -y wget httpd php gcc glibc glibc-common gd gd-devel make net-snmp
#yum install   httpd php  gd gd-devel gcc glibc glibc-common openssl perl perl-devel makesasa
Download Nagios Core and Nagios Plugins Tarballs
For all systems, run the following commands in your terminal:
cd /tmp
#wget http://prdownloads.sourceforge.net/sourceforge/nagios/nagios-4.0.4.tar.gz
#wget http://nagios-plugins.org/download/nagios-plugins-2.0.tar.gz
This will download Nagios Core, and it’s required plugins.
Adding the Nagios User and Group
Next add the appropriate user and group for the Nagios process to run:
#useradd nagios
#groupadd nagcmd
#usermod -a -G nagcmd nagios
Nagios Core Installatiom
#tar zxvf nagios-4.0.4.tar.gz
#tar zxvf nagios-plugins-2.0.tar.gz
Change to the new Nagios directory and install the packages:
#cd nagios-4.0.4
#./configure --with-command-group=nagcmd
#make all
#make install
#make install-init
#make install-config
#make install-commandmode
#make install-webconf
#cp -R contrib/eventhandlers/ /usr/local/nagios/libexec/
#chown -R nagios:nagios /usr/local/nagios/libexec/eventhandlers
#/usr/local/nagios/bin/nagios -v /usr/local/nagios/etc/nagios.cfg
#/etc/init.d/nagios start
For RHEL/CentOS users:
#/etc/init.d/httpd start
#systemctl start httpd
Create a Default User for Web Access.
Add a default user for Web Interface Access:
#htpasswd -c /usr/local/nagios/etc/htpasswd.users nagiosadmin
Nagios Plugin Installation
#cd /tmp/nagios-plugins-2.0
#./configure --with-nagios-user=nagios --with-nagios-group=nagios
#make
#make install
Nagios Service Setup
The following commands will register the Nagios daemon to be run upon system startup.
chkconfig --add nagios
chkconfig --level 35 nagios on
chkconfig --add httpd
chkconfig --level 35 httpd on
Nagios Web Interface
After correctly following the procedures you should now
be able to access your Nagios Core installation from a
web browser.
Simply use the following:
http://<your.nagios.server.ip>/nagios
And log in with the credentials you chose when adding
the nagiosadmin user to the htpasswd.users file.
Finishing
Como instalar Splunk 6.3.2 no CentOS Minimal 7.0
Olá amigos, segue um guia de como realizar a instação do Splunk
Efetuar o dowload do pacote de instalação.
#yum update
#yum install wget – Instalação do Wget

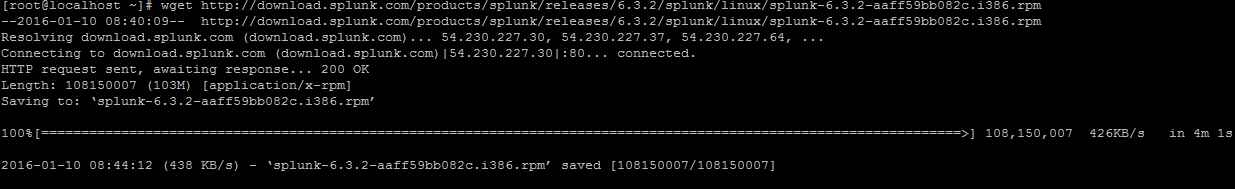
#wget http://download.splunk.com/products/splunk/releases/6.3.2/splunk/linux/splunk-6.3.2-aaff59bb082c.i386.rpm
Realizar a instalação do pacote .rpm.
#rpm -Uvh “pacote””splunk-6.3.2-aaff59bb082c.i386.rpm”
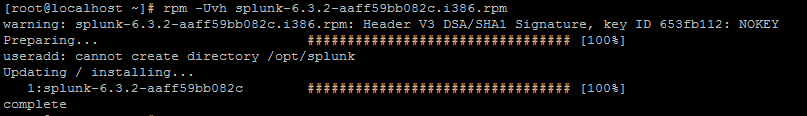
Instalando componentes
#yum -y install glibc.i686
Liberando portas no Firewall
Liberar porta web tcp 8000, syslog na udp 5514
#firewall-cmd –zone=public –permanent –add-port=8000/tcp
#firewall-cmd –zone=public –permanent –add-port=5514/udp
Forward syslog input to high port for non-root, allow port 80 for http
#firewall-cmd –direct –permanent –add-rule ipv4 nat PREROUTING 0 -p udp -m udp \–dport 514 -j REDIRECT –to-ports 5514
#firewall-cmd –direct –permanent –add-rule ipv4 nat PREROUTING 0 -p tcp -m tcp \–dport 80 -j REDIRECT –to-ports 8000
Reiniciar o firewall
#firewall-cmd –reload
Acessar o Diretorio de inicialização dentro do Splunk /opt/splunk/bin
#./splunk start –accept-license “Iniciar o Splunk e aceitar todos os termos”
#./splunk enable boot-start ” Colocar o Splunk na inicialização”.
O Splunk pode ser acessado através da URL http://ipserver:8000/